

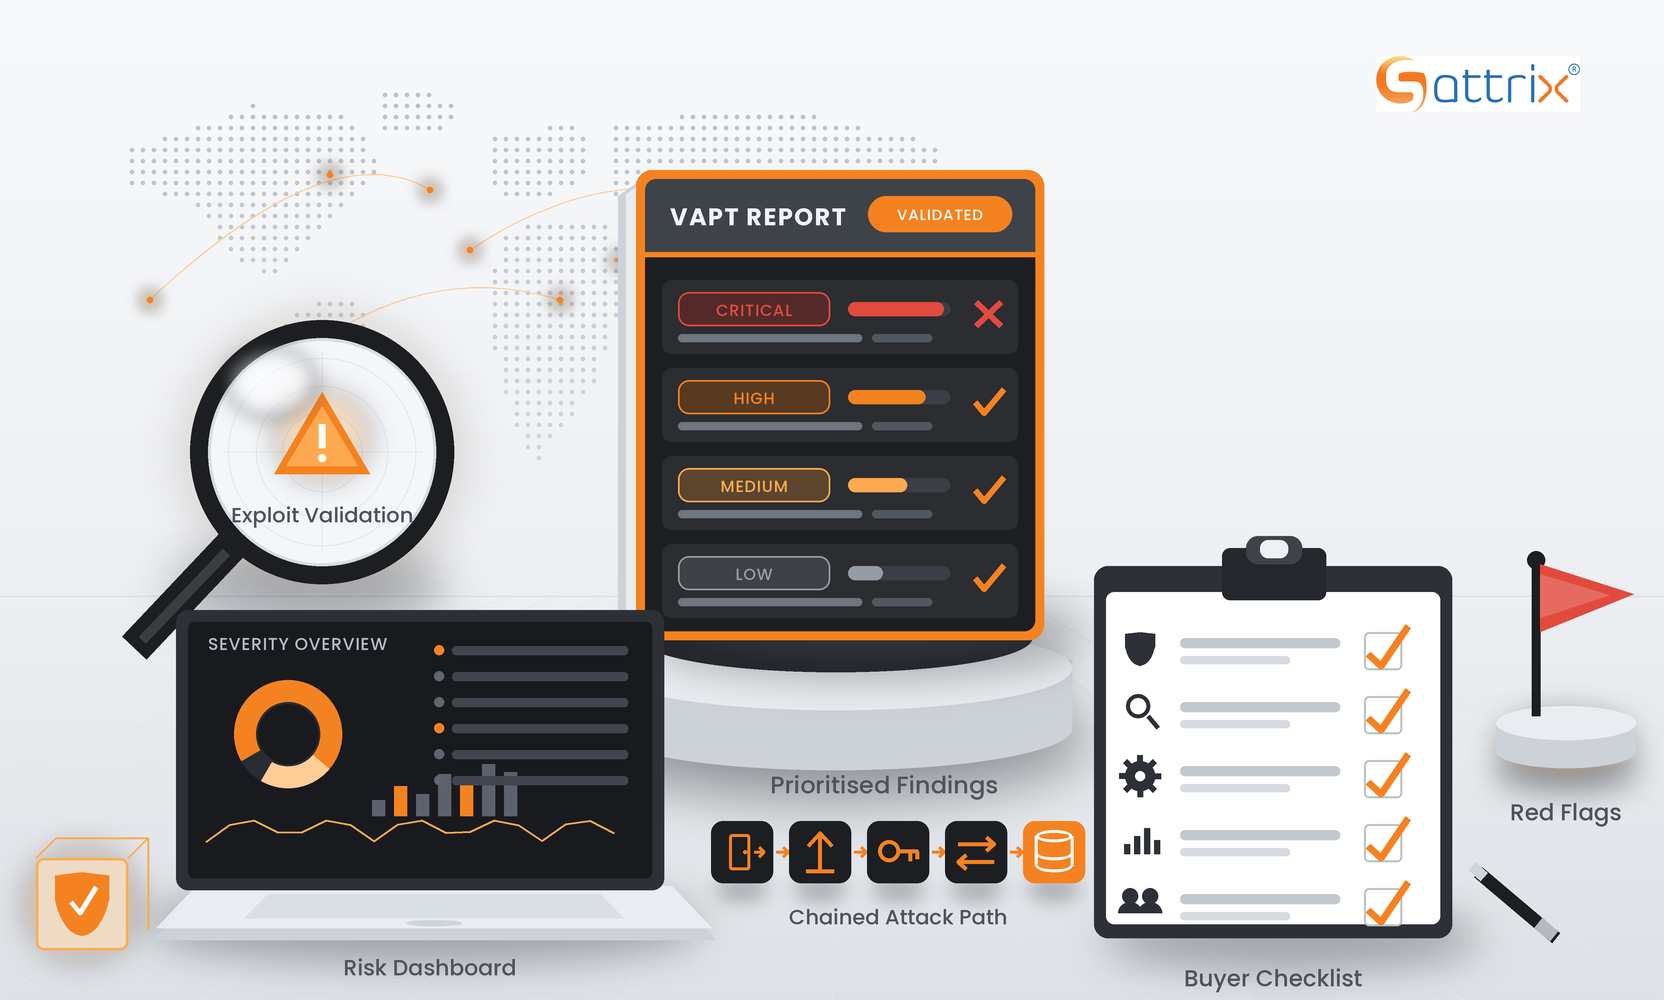
Most security assessments end the same way: a document lands in an inbox, gets circulated, and then competes for attention against everything else on the roadmap. Whether the issues inside it ever get fixed depends less on how many vulnerabilities were found and more on how clearly, they were written up.
A testing report is a decision-making instrument, not a deliverable to be filed away. It determines whether security issues are understood, prioritised, assigned to an owner, and remediated. It is also the clearest available evidence of how the engagement was conducted.
A strong security testing report has to work for three groups of readers at the same time. Reports usually fail because they serve one and ignore the other two.
Technical teams need reproducible evidence. They are not looking for reassurance; they need to know what was discovered, where it was found, how it was validated, and how to fix it. That means affected assets, technical proof, the steps used during the attack, and remediation guidance specific enough to act on.
Security managers do not need a longer list of vulnerabilities. They need prioritised risk. Findings should be ranked using severity, exploitability, exposure, business context, and the attack paths they enable. This is also where a report should show why three medium-severity issues can become a serious problem once they are chained together.
Executives need impact expressed in commercial and operational terms: potential financial loss, operational disruption, regulatory exposure, reputational damage, customer impact, or loss of sensitive information. Burying that translation under packet captures and payloads defeats the purpose.
The summary is the part most leaders will read, and sometimes the only part. A useful one covers:
Written properly, this section lets leadership understand the security situation, and decide what to fund, without reading the technical chapters.
Scope is where a professional assessment separates itself from a generic scan. The document should state:
Explicitly stating what was not tested is a marker of rigour, not a weakness. A report that implies total coverage of a complex environment within a short engagement is making a claim no tester can support. Residual risk is easier to manage when it is documented.
Methodology is how a buyer judges testing depth. Look for evidence of:
The distinction that matters is between meaningful security testing and automated scanning presented as a service. Scanners find known signatures. They do not find broken authorisation logic, flawed workflows, or the sequence of small weaknesses that leads to a domain compromise.
A typical VAPT report format organises each significant finding around a consistent structure, which makes triage far faster for engineering teams:
| Field | Purpose |
| Finding title | A short, specific description of the issue |
| Description | What the weakness is and why it exists |
| Affected asset | Exact host, URL, endpoint, or component |
| Severity and risk rating | Technical severity plus contextual risk |
| Evidence | Screenshots, requests, responses, or logs |
| Technical impact | What an attacker gains technically |
| Business impact | What the organisation stands to lose |
| Exploitation details | How the issue was actually abused |
| Reproduction steps | A path the internal team can follow |
| Root cause | The underlying flaw, where identifiable |
| Remediation | Specific, practical corrective action |
| References | Standards or advisories, where relevant |
Consistency here is not cosmetic. When every entry follows the same shape, teams can assign, estimate, and verify work without going back to the tester for basic clarification.
Identifying a potential vulnerability and proving it can be exploited are two different claims. Treating them as equivalent is how organisations end up spending sprint capacity on issues that were never reachable.
Validated findings should include:
Validation raises confidence in the whole assessment. It separates theoretical exposure from demonstrated risk, and it gives internal teams a defensible basis for pushing an urgent fix through change control.
Vulnerabilities assessed in isolation almost always understate real risk. Attackers do not work through a severity-sorted list; they look for a route.
Consider a common sequence:
Individually, nothing in that list would command board attention. Combined, it is a data breach. Attack-path analysis is one of the strongest indicators of mature penetration testing, because it requires the tester to think about the environment rather than the finding.
Severity scores are a useful starting point and a poor stopping point. The same CVSS rating can describe an urgent problem in one environment and a negligible one in another.
Risk is shaped by:
A high-severity issue on an isolated test system rarely outranks a medium-severity flaw on a customer-facing payment service. A good assessment report makes that comparison for the reader, so the organisation knows what to fix first and why.
Recommendations are where many otherwise competent reports lose their value. Guidance is actionable when it:
“Improve security controls” and “update configurations” are not recommendations. “Enforce server-side authorisation checks on the /api/v2/orders endpoint, so object ownership is validated against the session identity” is.
Weaknesses in a report are usually symptoms of process failure rather than presentation problems. Warning signs include:
Each of these should prompt a direct question: if this is the record of the engagement, what was done during it? A tester who validated exploitation has evidence. A tester who analysed attack paths has narratives. Absence tends to be informative.
The report is the most reliable sample of a provider’s work, more so than a capability deck. Organisations comparing vendors can work through a short checklist against a sanitised sample:
Providers with CREST-accredited testing practices, Sattrix among them, are generally willing to share a redacted sample for exactly this purpose. A reluctance to do so is itself a data point.
The value of a security assessment is not the number of vulnerabilities discovered. Volumes are easy to generate and easy to ignore.
The value lies in whether the document gives technical teams enough evidence to fix issues, security leaders enough context to prioritise them, and executives enough business understanding to make informed decisions. A high-quality assessment shows not only what was found, but how it was tested, what could be exploited, what the findings mean commercially, what was not tested, and what the organisation should do next.
Report quality is a proxy for engagement quality. Read it accordingly.
At minimum: an executive summary, defined scope and exclusions, a documented methodology, detailed findings with evidence and reproduction steps, severity and business-context-based risk ratings, attack-path analysis, and specific remediation guidance.
Evidence and reproducibility. A good report lets an engineer confirm each finding independently, shows how issues were exploited, and explains what the result means for the business rather than only assigning a score.
Yes, wherever exploitation was attempted and successful. Proof distinguishes demonstrated risk from theoretical exposure and helps teams justify urgent remediation. Where exploitation was not attempted, for example on production systems, the report should say so.
Because attackers chain weaknesses together. Several low and medium findings can combine into full compromise, and that outcome is invisible if each issue is assessed in isolation.
By combining technical severity with exposure, asset criticality, data sensitivity, exploitability, and regulatory impact. A medium-severity issue on a critical external system often warrants faster action than a high-severity issue on an isolated internal host.
Copy-pasted findings, scanner output with no manual validation, no evidence, no scope or methodology detail, identical recommendations across unrelated issues, and no prioritisation.
Request a sanitised sample and assess it as a work product. Methodology depth, exploit validation, attack-path analysis, and remediation specificity reveal how the provider works. Firms such as Sattrix that operate accredited testing practices typically expect this level of scrutiny during evaluation.


