

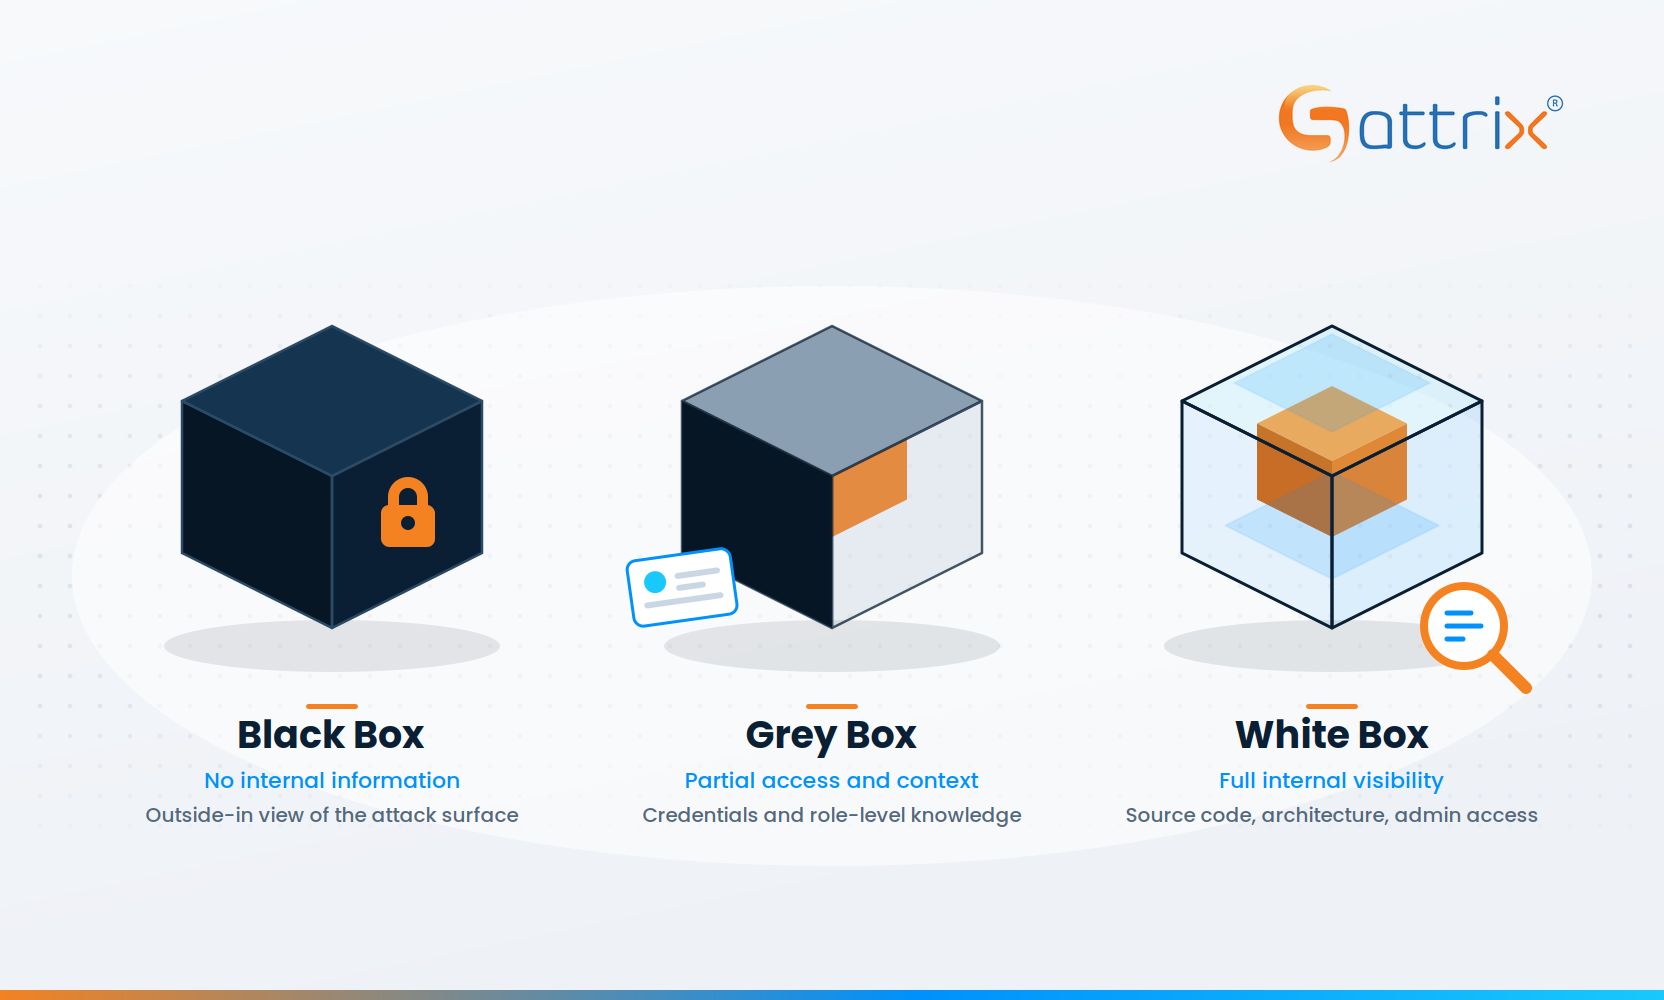
Every penetration test begins with a decision that sounds technical but is really a business choice: how much will you tell the testers?
Some organizations withhold everything, believing that a tester who knows nothing will behave like a real attacker. Others hand over credentials, architecture diagrams, and source code, expecting that more visibility will surface more issues. Both camps tend to argue about which approach is “more realistic.”
That argument usually leads nowhere, because realism is not what a test is bought for. Assurance is. The useful question is not which method is closest to an attacker’s experience, but which method answers the security question your organization needs answered, within the time and budget available.
This article looks at the three main VAPT testing methods, what each one can and cannot validate, and how to select between them using your assurance objective rather than instinct.
The three labels describe how much information and access the testing team receives before work begins.
| Method | Information provided | Typical starting point |
| Black box | Little or none beyond a target scope | Domain names, IP ranges, or an application URL |
| Grey box | Partial internal knowledge | User credentials, role descriptions, basic architecture notes, API documentation |
| White box | Extensive internal detail | Source code, design documents, admin credentials, infrastructure configuration, data flow diagrams |
These are points on a spectrum rather than three rigid categories. Most real engagements sit somewhere in between, and scope documents often mix them. An external network test may be black box while the application inside it is tested with credentials.
The technical work also overlaps heavily. All three use similar tooling, similar manual techniques, and similar exploitation methods. What changes is where the testing hours go.
Black box testing evaluates what someone outside your organization can discover and exploit from your exposed attack surface.
It is well suited to questions such as:
Black box work is also useful when you want to test detection and response, since the testing team’s noisy reconnaissance gives your SOC something to catch.
The limitations are structural rather than a matter of tester skill. Without credentials, a tester cannot examine authenticated workflows. Without role context, they cannot verify whether a finance user can reach HR records. Without source code, they cannot see an insecure deserialization path, or a hardcoded secret buried in a rarely triggered branch. Business logic flaws, privilege escalation chains, and authorization gaps mostly live behind a login page.
So, a clean black box report does not mean the application is sound. It means nothing exploitable was found from the outside within the hours allocated.
Grey box testing gives testers partial knowledge, most commonly a set of user accounts at different privilege levels, plus enough documentation to understand how the application is meant to work.
That small amount of context changes the shape of the engagement. Instead of spending the first several days mapping the application from the outside, testers begin inside it and spend those hours validating controls.
Grey box testing is often selected for:
It also reflects a common real-world scenario. Attackers frequently arrive with valid credentials obtained through phishing, credential stuffing, or a third-party breach. Testing from that position is not a shortcut. It is a legitimate threat model.
White box testing provides testers with source code, architecture documentation, configuration files, and privileged access.
This supports the most systematic assessment available. Testers can trace how input travels through the application, review cryptographic implementation, examine authentication logic line by line, inspect dependency handling, and identify flaws that would be impractical to find by probing from the outside. Coverage becomes measurable, because you can see which components were reviewed and which were not.
White box testing suits high-assurance situations: payment systems, healthcare platforms, custom cryptography, pre-release review of a major build, and regulated environments where evidence of thorough review matters.
Its limitations are different. Full visibility does not reproduce every attacker scenario. A code review will not tell you whether your monitoring would notice exploitation, whether an exposed staging server is advertising an old version of the application, or how the system behaves under the messy conditions of production. Depth in one dimension is not breadth across all of them.
The case for black box testing often rests on realism. A real attacker starts with nothing, so the tester should start with nothing.
The comparison breaks down on the variable that matters most, which is time.
Incident response data consistently shows attackers spending substantial periods inside environments before detection, frequently weeks and sometimes months. During that dwell time an attacker can watch traffic patterns, collect credentials gradually, study how administrators work, wait for a maintenance window, and try approaches that would be far too slow or too noisy for a scheduled engagement. Their reconnaissance is not limited to a statement of work.
A penetration test typically runs for one to three weeks, with agreed rules of engagement, a fixed target list, and a requirement to avoid disrupting production.
So, a time-boxed black box test does not recreate attacker conditions simply by starting with limited information. It recreates a compressed and constrained version of the earliest phase of an intrusion. That phase is worth testing, and the exercise is worth doing. It just should not be mistaken for a full simulation of a patient adversary.
Treating “less information” as automatically more rigorous can quietly reduce assurance. You may pay for a specialist team and spend a third of the engagement on discovery work that your own asset inventory could have supplied in an afternoon.
A more practical way to think about the black box vs grey box vs white box testing decision is to treat access as a budget allocation lever.
Every engagement has a fixed number of hours. Those hours split between two activities:
Information you provide upfront moves hours from the first column into the second. If you give testers a list of in-scope endpoints, valid accounts for each role, and a short walkthrough of the business workflow, you are not making the test easier in a way that weakens it. You are buying more validation for the same money.
This framing is useful for security leaders defending a testing budget, because it reframes the discussion from “how hard did we make it for the testers” to “how much depth did we get per rupee or dollar spent.”
Rather than ranking the methods, map your business question to the approach that answers it.
| Business question | Suitable approach |
| What can an external attacker discover and exploit? | Black box |
| What weaknesses are visible from our external attack surface? | Black box |
| Can an attacker with limited internal knowledge escalate access? | Grey box |
| How effective are authentication and authorization controls with realistic user access? | Grey box |
| Are vulnerabilities hidden within application logic or source code? | White box |
| Are there weaknesses that require internal visibility to identify? | White box |
| How deeply can this application be assessed within a fixed budget? | Grey or white box, depending on objective |
These are decision mappings, not rules. The right choice also depends on your threat model, the application type, the sensitivity of the data involved, your testing window, regulatory expectations, and the level of assurance your board or customers require. Engagements that assessment teams at providers such as Sattrix scope well tend to begin with that objective written down before any method is chosen.
Yes, and mature programmes usually do.
A common pattern is a black box external test once or twice a year to check the perimeter and exercise detection, combined with grey box testing on each significant application release, and white box review reserved for high-risk components or major architectural changes.
Staged engagement is another option. Testers begin black box, document what was reachable without help, then receive credentials and documentation partway through so the remaining time goes into depth. You get both perspectives from one engagement, with a clear record of which findings came from which phase.
There is not universally best VAPT method. Black boxes, grey boxes, and white box testing answer different questions, carry different blind spots, and consume the same testing hours in different proportions.
Decide what you need evidence for. Set the access level that gets you there efficiently. Then judge the engagement on scope, execution quality, and the usefulness of the findings rather than on how little the testers were told.
The difference is the information testers receive. Black box provides minimal detail, grey box provides partial internal knowledge such as user credentials, and white box provides extensive access including source code and architecture documentation.
Not automatically. Real attackers operate over long periods and gather information continuously. A short black box engagement reproduces a constrained version of early reconnaissance, not the full conditions of a determined intrusion.
Grey box testing is a common default for web applications, because most meaningful risk sits behind authentication. Black box testing adds value for the exposed surface, and white box review suits sensitive or custom-built components.
When the question involves authenticated behaviors: role separation, privilege escalation, authorization boundaries, business logic, or the impact of a compromised user account.
It usually finds more code-level and logic-level issues because visibility is higher. It will not necessarily reveal exposure, configuration of drift, or detection gaps that only appear from an external viewpoint.
Yes. Many organizations run them in sequence or in a single staged engagement, starting with no information and adding access partway through so that both external exposure and internal depth are covered.
Start with the security question and the assurance you need to demonstrate. Match that to the access model that answers it within your testing window and budget, then confirm that scope and reporting quality meet your requirements.


